Cybersecurity for Productivity Tools: Essential Protections for US Professionals in 2026 to Prevent 99% of Data Breaches
In the rapidly evolving digital landscape of 2026, productivity tools have become the backbone of operations for US professionals across every industry. From collaborative documents and project management platforms to communication suites and CRM systems, these tools are indispensable for daily tasks, fostering innovation, and maintaining competitive edge. However, their widespread adoption has also made them prime targets for cybercriminals, leading to an escalating threat of data breaches. The stakes are higher than ever, with compromised data potentially leading to significant financial losses, reputational damage, and severe legal repercussions. Therefore, implementing robust productivity tool security measures is not merely an option but a critical imperative for organizations aiming to prevent 99% of data breaches and safeguard their most valuable assets.
This comprehensive guide delves into the essential cybersecurity protections that US professionals must adopt in 2026. We will explore the current threat landscape, dissect the vulnerabilities inherent in popular productivity tools, and provide actionable strategies to fortify your digital defenses. Our goal is to equip you with the knowledge and tools necessary to navigate the complex world of cyber threats, ensuring your productivity remains unhindered while your data stays secure.
The Evolving Threat Landscape: Why Productivity Tool Security is More Critical Than Ever
The year 2026 presents a cybersecurity landscape characterized by increasing sophistication and frequency of attacks. Cybercriminals are no longer relying solely on broad phishing campaigns; they are employing advanced tactics such as AI-powered social engineering, supply chain attacks, and sophisticated ransomware variants specifically designed to exploit vulnerabilities in widely used software. Productivity tools, by their very nature, handle a vast amount of sensitive information, from confidential business plans and intellectual property to personal employee data and customer records. This makes them incredibly attractive targets. A single breach can expose millions of records, leading to devastating consequences.
Key Threats Targeting Productivity Tools:
- Phishing and Social Engineering: Highly personalized and convincing attacks that trick users into revealing login credentials or downloading malicious software.
- Malware and Ransomware: Malicious programs designed to disrupt operations, steal data, or encrypt files until a ransom is paid.
- Insider Threats: Data breaches caused by negligent or malicious employees with access to sensitive information within productivity platforms.
- API Vulnerabilities: Weaknesses in the Application Programming Interfaces (APIs) that allow different productivity tools to communicate, creating potential entry points for attackers.
- Supply Chain Attacks: Compromising a vendor or third-party service provider that integrates with your productivity tools, thereby gaining access to your systems.
- Cloud Configuration Errors: Misconfigurations in cloud-hosted productivity suites that inadvertently expose data to the public internet.
Understanding these threats is the first step towards building a resilient productivity tool security framework. The dynamic nature of cyber threats demands continuous vigilance and adaptation of security strategies.
Baseline Protections: The Foundation of Strong Productivity Tool Security
Before diving into advanced strategies, it’s crucial to establish a solid foundation of baseline security practices. These fundamental measures are often overlooked but are essential for preventing a vast majority of common attacks.
1. Implement Strong Authentication Mechanisms
Weak passwords remain one of the easiest entry points for cybercriminals. Strengthening authentication is paramount.
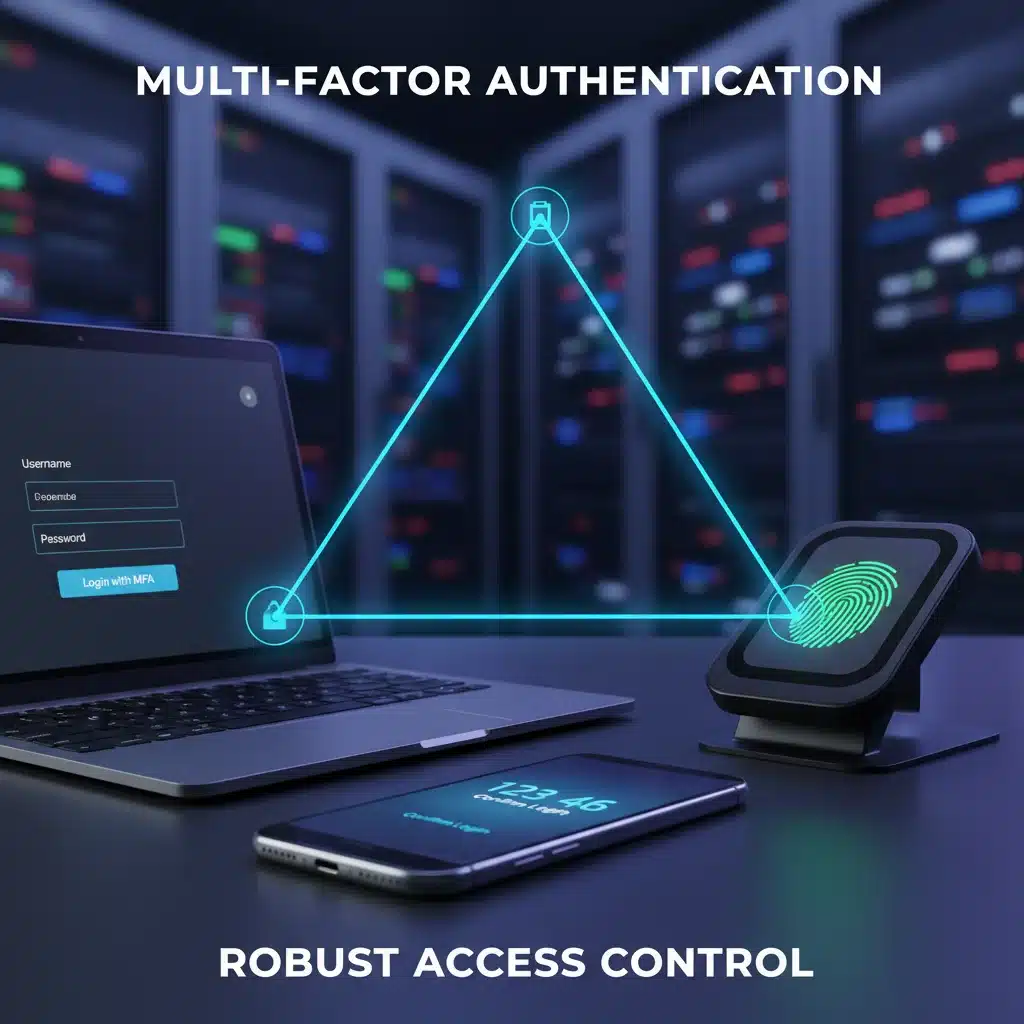
- Multi-Factor Authentication (MFA): Mandate MFA for all user accounts across all productivity tools. This adds an extra layer of security, requiring users to provide two or more verification factors to gain access, such as a password and a code from a mobile app, or a biometric scan. Even if a password is compromised, MFA prevents unauthorized access.
- Single Sign-On (SSO): Implement SSO solutions to streamline user access while centralizing authentication management. This reduces password fatigue and allows for easier enforcement of strong password policies and MFA.
- Password Policies: Enforce strong, unique passwords for all accounts. Policies should dictate minimum length, complexity requirements (uppercase, lowercase, numbers, symbols), and regular password rotations. Password managers should be encouraged or provided.
2. Regular Software Updates and Patch Management
Software vulnerabilities are frequently discovered and exploited by attackers. Keeping all productivity tools and operating systems up-to-date is non-negotiable for effective productivity tool security.
- Automated Updates: Configure tools and systems for automatic updates whenever possible.
- Patch Management Strategy: Establish a robust patch management program to identify, test, and deploy security patches promptly across all devices and software.
- Vulnerability Scanning: Regularly scan your systems and applications for known vulnerabilities and address them proactively.
3. Data Encryption at Rest and in Transit
Encryption renders data unreadable to unauthorized parties, even if they manage to gain access to your systems. This is a cornerstone of modern productivity tool security.
- Encryption in Transit: Ensure all data exchanged between users and productivity tools, and between different tools, is encrypted using protocols like TLS (Transport Layer Security).
- Encryption at Rest: Verify that data stored within productivity tools, whether on cloud servers or local devices, is encrypted. Many cloud providers offer this by default, but it’s crucial to confirm and configure it correctly.
- Endpoint Encryption: Encrypt hard drives of all devices used to access productivity tools (laptops, desktops, mobile devices).
Advanced Strategies for Fortifying Productivity Tool Security in 2026
Beyond the baseline, organizations must adopt more sophisticated strategies to counter advanced persistent threats and achieve near-perfect data breach prevention.
1. Granular Access Control and Least Privilege
Not everyone needs access to everything. Implementing granular access controls based on the principle of least privilege significantly reduces the attack surface.
- Role-Based Access Control (RBAC): Define specific roles within your organization and assign permissions based on those roles. Users should only have access to the data and functionalities absolutely necessary for their job responsibilities.
- Just-in-Time (JIT) Access: For highly sensitive data or administrative functions, implement JIT access, where permissions are granted only for a limited time when needed, and then automatically revoked.
- Regular Access Reviews: Periodically review user access rights to ensure they are still appropriate and revoke access for employees who have changed roles or left the company.
2. Data Loss Prevention (DLP) Solutions
DLP solutions are designed to prevent sensitive information from leaving the organization’s control, whether intentionally or accidentally. This is critical for robust productivity tool security.
- Content Monitoring: DLP tools can monitor content within emails, cloud storage, and collaborative documents for sensitive data patterns (e.g., credit card numbers, social security numbers, proprietary keywords).
- Policy Enforcement: Establish policies that automatically block, encrypt, or alert administrators when sensitive data attempts to be shared externally or stored in unapproved locations.
- User Education: While DLP provides technical controls, educating users about data handling policies is equally important to prevent accidental data leaks.
3. Cloud Security Posture Management (CSPM)
Many productivity tools are cloud-based. Misconfigurations in cloud environments are a leading cause of data breaches. CSPM tools continuously monitor cloud environments for security risks and compliance violations.
- Continuous Monitoring: CSPM solutions automatically scan cloud configurations against established security benchmarks and best practices.
- Automated Remediation: Some CSPM tools can automatically remediate identified misconfigurations or provide detailed instructions for manual fixes.
- Compliance Assurance: CSPM helps ensure that your cloud-based productivity tools comply with relevant industry regulations and standards.
4. Endpoint Detection and Response (EDR)
While productivity tools are often cloud-based, the endpoints (laptops, desktops, mobile devices) from which they are accessed remain critical points of vulnerability. EDR solutions provide advanced threat detection and response capabilities for these devices.
- Real-time Monitoring: EDR continuously monitors endpoint activities for suspicious behavior, such as unauthorized access attempts, unusual file modifications, or malicious process executions.
- Automated Response: Upon detecting a threat, EDR can automatically isolate the affected endpoint, terminate malicious processes, or roll back system changes to a pre-infection state.
- Threat Hunting: EDR tools allow security teams to proactively search for hidden threats within their endpoints, enhancing overall productivity tool security.
5. Secure API Integrations and Third-Party Risk Management
The interconnected nature of modern productivity suites means that vulnerabilities in one integrated service can impact others. Managing third-party risks and securing API integrations are crucial.
- API Security Gateways: Implement API security gateways to control and monitor access to APIs, enforce security policies, and detect abnormal usage patterns.
- Vendor Security Assessments: Thoroughly vet the security practices of all third-party vendors whose services integrate with your productivity tools. This includes reviewing their security certifications, incident response plans, and data handling policies.
- Contractual Agreements: Ensure that service level agreements (SLAs) with vendors include clear cybersecurity requirements, incident notification clauses, and audit rights.
User Education and Awareness: The Human Firewall
Even the most sophisticated technical controls can be undermined by human error. Employees are often the first and last line of defense, making comprehensive user education indispensable for effective productivity tool security.
1. Regular Security Training
Conduct mandatory and engaging security awareness training sessions for all employees, covering topics such as:
- Phishing Recognition: How to identify and report phishing, spear-phishing, and whaling attempts.
- Password Hygiene: Best practices for creating strong, unique passwords and using password managers.
- Data Handling Policies: Guidelines for handling sensitive information, including what data can be stored where and how it should be shared.
- Device Security: Secure use of personal and company devices, including public Wi-Fi risks and physical security.
- Incident Reporting: Clear procedures for reporting suspicious activities or potential security incidents.
2. Simulated Phishing Attacks
Regularly conduct simulated phishing campaigns to test employee vigilance and reinforce training. Provide immediate feedback and additional training to those who fall for the simulations.
3. Fostering a Security-First Culture
Beyond formal training, cultivate a culture where security is everyone’s responsibility. Encourage employees to be proactive about security, ask questions, and report concerns without fear of reprisal. Leadership should visibly champion security initiatives.
Incident Response and Business Continuity Planning
Despite all preventative measures, a breach can still occur. Having a well-defined incident response plan is crucial for minimizing damage and ensuring business continuity. This is a vital component of holistic productivity tool security.
1. Develop a Comprehensive Incident Response Plan (IRP)
An IRP outlines the steps an organization will take before, during, and after a cybersecurity incident. Key components include:
- Preparation: Defining roles and responsibilities, establishing communication channels, and gathering necessary tools.
- Identification: Procedures for detecting and confirming a security incident.
- Containment: Steps to limit the scope and impact of the incident, such as isolating affected systems.
- Eradication: Removing the root cause of the incident and eliminating threats.
- Recovery: Restoring affected systems and data to normal operations.
- Post-Incident Analysis: Learning from the incident to improve future security measures.
2. Regular Backups and Recovery Strategies
Implement a robust data backup strategy for all critical data stored in productivity tools. Ensure backups are:
- Regularly Performed: Automated and frequent backups.
- Isolated: Stored separately from the primary network to prevent ransomware from encrypting backups.
- Tested: Periodically tested to ensure data can be successfully restored.
3. Business Continuity and Disaster Recovery (BCDR)
Beyond data recovery, BCDR plans ensure that critical business functions can continue during and after a significant disruption, including cyberattacks. This involves identifying critical processes, developing alternative operational methods, and regularly testing the plan.
Emerging Trends in Productivity Tool Security for 2026
The cybersecurity landscape is constantly evolving. Staying ahead requires understanding and adapting to emerging trends.
1. Zero Trust Architecture (ZTA)
Zero Trust operates on the principle of ‘never trust, always verify.’ Instead of trusting users or devices within a network perimeter, ZTA requires continuous verification of every access attempt, regardless of location. Implementing ZTA for productivity tools means:
- Strict Identity Verification: Every user and device must be authenticated and authorized before accessing resources.
- Least Privilege Access: Users are granted only the minimum access necessary for their tasks.
- Micro-segmentation: Networks are divided into small, isolated segments to limit lateral movement of threats.
- Continuous Monitoring: All activities are continuously monitored for suspicious behavior.
Adopting a Zero Trust model significantly enhances productivity tool security by assuming compromise and focusing on granular verification.
2. AI and Machine Learning in Cybersecurity
AI and ML are transforming cybersecurity by enabling faster threat detection, more accurate anomaly identification, and automated response capabilities.
- Behavioral Analytics: AI can analyze user behavior patterns to detect deviations that might indicate a compromised account or insider threat.
- Threat Intelligence: ML algorithms can process vast amounts of global threat data to predict emerging attack vectors and vulnerabilities.
- Automated Incident Response: AI-powered tools can automate aspects of incident response, reducing the time to detect and contain breaches.
3. Enhanced Supply Chain Security
As organizations become more reliant on third-party software and services, securing the supply chain is paramount. This includes rigorous vetting of vendors, continuous monitoring of third-party risks, and ensuring secure software development lifecycles (SSDLC) from all suppliers.
4. Data Sovereignty and Compliance
For US professionals, compliance with various data protection regulations (e.g., HIPAA, GDPR for data processed from EU citizens, CCPA) is critical. Understanding where data is stored and processed by productivity tools, and ensuring these locations comply with relevant data sovereignty laws, is a growing concern.
Choosing the Right Productivity Tools with Security in Mind
The security of your productivity tools begins with the selection process itself. When evaluating new tools or reviewing existing ones, consider the following security-centric criteria:
1. Built-in Security Features
Prioritize tools that offer robust, built-in security features rather than relying solely on third-party add-ons. Look for:
- Native MFA support
- End-to-end encryption
- Granular access controls and audit trails
- Data loss prevention capabilities
- Regular security audits and certifications (e.g., ISO 27001, SOC 2 Type 2)
2. Vendor’s Security Posture
Investigate the security practices of the tool vendor. This includes their:
- Incident Response Plan: How do they handle security incidents?
- Data Privacy Policy: How do they protect your data and comply with regulations?
- Transparency: Are they open about their security practices and any past breaches?
- Security Team: Do they have a dedicated security team and robust security development lifecycle?
3. Integration Security
Assess how the tool integrates with your existing IT ecosystem. Insecure integrations can create new vulnerabilities. Ensure APIs are well-documented, secured with proper authentication, and limited to necessary permissions.
4. Customization and Flexibility
While off-the-shelf solutions are convenient, ensure they offer enough customization to align with your organization’s specific security policies and compliance requirements. Rigidity can sometimes lead to security gaps.
Conclusion: A Proactive Approach to Productivity Tool Security
Achieving 99% prevention of data breaches in 2026 for US professionals hinges on a proactive, multi-layered approach to productivity tool security. It’s not about implementing a single solution but rather integrating a comprehensive strategy that encompasses strong technical controls, continuous monitoring, robust incident response, and, crucially, a security-aware workforce. By prioritizing strong authentication, regular updates, data encryption, granular access controls, and leveraging advanced technologies like Zero Trust and AI, organizations can significantly reduce their attack surface and protect their invaluable data. The digital landscape will continue to evolve, bringing new threats and challenges. However, with persistent vigilance, continuous adaptation, and a commitment to cybersecurity best practices, US professionals can confidently leverage the power of productivity tools while safeguarding their operations against the ever-present threat of cyberattacks.
Remember, security is an ongoing journey, not a destination. Regular reviews, updates, and training are essential to maintain a strong defense. By embedding security into the very fabric of how productivity tools are used and managed, organizations can not only prevent breaches but also foster an environment of trust, resilience, and sustained success in the digital age.